Claude Code is an agentic coding tool that reads and modifies files and runs commands in a development environment. CVE-2026-39861 is a sandbox escape vulnerability affecting versions of Claude Code prior to 2.1.64. A process running inside the sandbox could create a symbolic link to a location outside the workspace, allowing a subsequent file write by Claude Code’s unsandboxed process to reach that location without prompting the user for confirmation.
Reliable exploitation requires untrusted content to enter the Claude Code context and trigger sandboxed code execution via prompt injection. Successful exploitation can result in arbitrary file writes outside the workspace and may lead to code execution on the host. Anthropic addressed the vulnerability in version 2.1.64, and users who manage updates manually should update to version 2.1.64 or later.
Tags: CVE-2026-39861, Claude Code, Anthropic, Sandbox Escape, Prompt Injection, Symbolic Link, Arbitrary File Write, CWE-22, CWE-61
---
1. Overview

Claude Code is an agent-based coding tool capable not only of reading and modifying source code but also of executing commands necessary for the development process. During command execution, it uses a sandbox to restrict file access and network communication, and to control actions that access resources outside the workspace.
This report addresses CVE-2026-39861, a symbolic link handling vulnerability discovered in Claude Code’s sandbox. This vulnerability occurs when a non-sandboxed Claude Code process follows a symbolic link created within the sandbox; a successful attack could allow an attacker to write a file to an arbitrary path outside the workspace.
CVE-2026-39861 affects versions of Claude Code prior to 2.1.64, and Anthropic has fixed the related issue in version 2.1.64.
---
2. Attack Type
CVE-2026-39861 is a sandbox escape vulnerability disclosed in April 2026. It is registered in the NVD as a path handling flaw (CWE-22) that allows access to paths outside a restricted directory and a UNIX symbolic link traversal flaw (CWE-61).
Sandbox Operation Structure
A symbolic link is a mechanism that allows a specific file or directory to be referenced from a different path. Claude Code’s sandbox restricted internal processes from writing files directly outside the sandbox, but it did not sufficiently block the creation of symbolic links pointing to external paths within the sandbox. Since the links themselves are created within the sandbox, the sandbox treated them as writes to permitted paths.
Cause of the Vulnerability
In this scenario, if a non-sandboxed process in Claude Code writes a file to the path specified by the link, the operating system resolves the symbolic link and performs the write operation at the actual location to which the link points. The key point is that it is not enough to simply verify whether the requested path is within the workspace; it is also necessary to double-check that the final resolved path—after all links have been resolved—is within the same boundary. In the vulnerable version, this verification was insufficient, allowing a write operation that began as a path within the workspace to reach an external file without undergoing any user verification.
Consequently, the sandboxed process creates only the link without writing directly to the external file, while the non-sandboxed process writes the file to a path that appears to be within the workspace. While each action individually appears to be within acceptable limits, the combination of these two actions results in a path verification discrepancy that circumvents the sandbox boundary.
Attack Flow
***Figure 1_.*CVE-2026-39861 Attack Flow and Sandbox Boundary Bypass Process_
- Untrusted content, such as repository files or documents created by an attacker, is included in the Claude Code context.
- A prompt injection embedded in this content triggers command execution within the sandbox.
- A Bash process running in the sandbox creates a symbolic link within the workspace that points to a path outside the workspace.
- Subsequently, when a file-writing function operating outside the sandbox attempts to write to that path, the operating system follows the link and modifies the actual target file outside the sandbox.
Exploitation Conditions and Impact
This vulnerability cannot be exploited simply by executing Claude Code. An attacker must be able to inject untrusted content into the Claude Code context, and conditions must be met for commands to be executed within the sandbox via prompt injection.
If the attack is successful, files outside the workspace can be created or overwritten within the scope of the user account running Claude Code.
- If shell initialization files, Git hooks, or editor settings are modified, the subsequent code may execute upon the next login or when development tools are launched.
- If configuration files related to SSH, cloud services, or package repositories are targeted, the scope of the impact could extend to development credentials and the supply chain.
The paths listed above are examples intended to illustrate potential impacts; the official advisory did not cite any actual attack cases involving specific files.
---
3. Mitigation Measures
Patches and Version Verification
Anthropic has addressed this vulnerability in Claude Code version 2.1.64. The fix has been automatically deployed to environments using standard automatic updates; in environments where versions are managed manually, you must verify the installed version yourself.
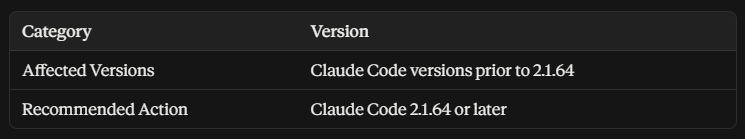
You can check your current version and perform a manual update using the following command.
claude --version
claude update
If installed via a package manager such as Homebrew, WinGet, or apk, you must follow the update procedure for each respective package manager.
The need to check for updates is not limited to developer devices. The environments listed below often do not receive automatic updates and must be checked separately.
- Developer devices with Claude Code installed
- CI/CD runner images with a fixed version
- Development container definition files
- Internal package mirrors and offline caches
Temporary Workarounds
If immediate updates are not feasible, you must restrict Claude Code from accessing untrusted repositories, documentation, issue descriptions, or build logs. If external content must be processed, users should manually review the file writes and shell commands that Claude Code attempts to execute to ensure there are no actions that reference paths outside the workspace or create unexpected symbolic links.
In managed environments, ensure that the system does not switch to non-isolated execution when the sandbox is not initialized sandbox.failIfUnavailableset to trueto prevent non-isolated retries of commands that failed due to sandbox restrictions, set sandbox.allowUnsandboxedCommandssetto falseto prevent non-isolated retries of commands that failed due to sandbox restrictions. While these settings do not replace security patches, they help reduce the risk of bypassed execution in environments where sandboxing is mandatory under operational policies.
In sensitive development environments, it is recommended to run Claude Code within a development container or a separate virtual environment. In such cases, do not mount critical files—such as the host’s SSH keys or cloud credentials—into the container, and limit external communication to only what is strictly necessary.
Verifying Compromise and Post-Incident Measures
If there is a history of processing external content using a version prior to the patch, you should check the following items:
- The actual paths pointed to by symbolic links within the workspace
- The timestamps and contents of shell initialization files, Git hooks, and SSH and cloud configuration files
- During a Claude Code session symlink() or symlinkat() any subsequent file writes to the same path following the call
The last item can be used as a detection criterion in environments that collect endpoint logs. If suspicious changes are detected, do not stop at file recovery; you must also replace the relevant SSH keys and access tokens.
Limitations from a network security perspective
This vulnerability does not arise from specific external HTTP requests directly triggering a web server vulnerability, but rather occurs during the file processing of the local Claude Code. Therefore, it is not suitable for direct detection or blocking via web application firewalls based on attack patterns; prioritizing Claude Code updates and endpoint access controls is more important than adding web attack patterns.
During the stage where malicious repositories or files are transmitted via the web, download controls and reputation checks can serve as supplementary defenses. However, since these measures alone cannot eliminate the symbolic link processing vulnerability, applying the patch should be the top priority.
---
4. Conclusion
CVE-2026-39861 is an arbitrary file write vulnerability that occurs when a non-sandboxed process follows a symbolic link created within the Claude Code sandbox. Although untrusted content must first enter the context and lead to command execution via prompt injection, a successful attack allows an attacker to modify files outside the workspace and execute subsequent code on the host without user verification.
Developer machines often contain not only source code but also SSH keys, cloud credentials, package repository tokens, and CI/CD access permissions. Therefore, writing to external files can lead not only to the tampering of the development environment but also to credential theft, the establishment of persistence, and compromise of the deployment environment.
In all environments using Claude Code versions earlier than 2.1.64, updating to the latest version should be the top priority. If external content was processed prior to applying the patch, check the symbolic links and change logs for critical files in the workspace; if any suspicious traces are found, replace the relevant credentials.
---